CipherWatch Home

Category

Account Security

6 articles

The Long Shadow of Stolen Credentials: Why Breaches From Years Ago Are Still Compromising Accounts Today

The Long Shadow of Stolen Credentials: Why Breaches From Years Ago Are Still Compromising Accounts Today

Changing a password after a data breach feels like a decisive act of self-protection. For millions of Americans, however, that single step leaves an extensive trail of downstream vulnerability entirely intact. Attackers have built an industrialized pipeline for converting years-old stolen credentials into active account takeovers — and the process is more automated, more scalable, and more profitable than most users appreciate.
Peer-to-Peer, Public by Default: The Privacy Gaps Hidden Inside America's Favorite Payment Apps

Peer-to-peer payment apps have become as routine as cash for millions of Americans, but the privacy trade-offs embedded in their default settings are rarely discussed at the point of signup. From publicly visible transaction feeds to aggressive data-sharing agreements with third-party advertisers, platforms like Venmo, Cash App, and Zelle expose users to risks that extend well beyond the occasional disputed charge. This investigation examines what these apps actually know about you, how fraudste

Broken by Design: How Outdated Password Rules Are Training Users to Fail

Broken by Design: How Outdated Password Rules Are Training Users to Fail

For decades, IT departments and websites have demanded passwords packed with symbols, capital letters, and numbers — convinced they were building stronger defenses. New research and updated federal guidance suggest the opposite may be true, and the habits those rules created could be putting millions of Americans at greater risk than ever.

Persistent Logins, Persistent Risks: The Hidden Danger Lurking in Your 'Stay Signed In' Button

Persistent Logins, Persistent Risks: The Hidden Danger Lurking in Your 'Stay Signed In' Button

That small checkbox offering to keep you signed in feels like a minor convenience, but it quietly creates a long-lived attack surface that cybercriminals know how to exploit. Session tokens stored on your device can be stolen, replayed, and weaponized — sometimes without your knowledge for months. This investigation breaks down how persistent authentication works, where it fails, and how to make smarter decisions about which services deserve your lasting trust.

Authentication Reckoning: How New Email Security Rules Affect Every Inbox in America

Authentication Reckoning: How New Email Security Rules Affect Every Inbox in America

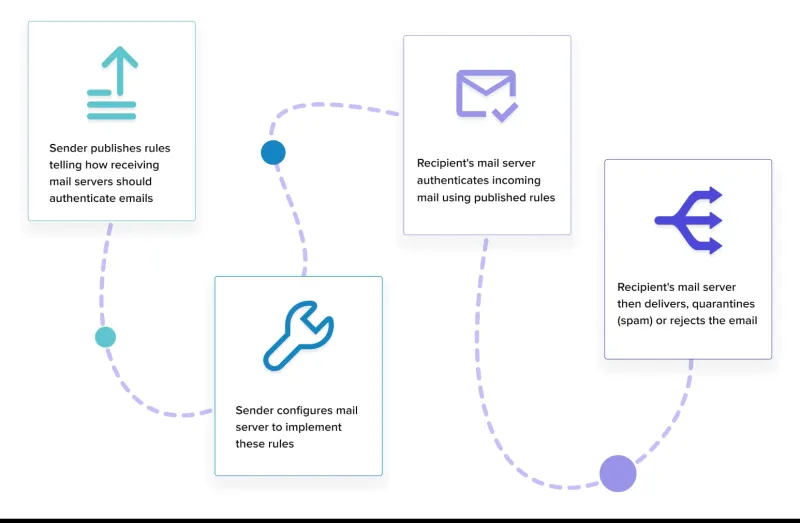
Gmail, Outlook, and Yahoo have begun enforcing long-standing email authentication protocols with unprecedented firmness, and the consequences extend far beyond bulk marketers. Understanding what SPF, DKIM, and DMARC actually do — and why providers are finally demanding compliance — could be the difference between your messages landing safely and vanishing into the void.

One Vault to Rule Them All: The Real Truth About Password Manager Security

One Vault to Rule Them All: The Real Truth About Password Manager Security

Password managers promise to solve the chaos of credential sprawl—but what happens when the vault itself becomes a target? From the LastPass breach to zero-knowledge encryption, we examine whether centralizing your digital keys is a calculated risk worth taking, and how to make that bet as safe as possible.